SAML
Contents
Where is this feature available?
Free / Open-source
Paid
Boost
Scale
Enterprise


Security Assertion Markup Language (SAML) enables users to access multiple systems with a single set of credentials. This is helpful for growing organizations that require centralized user management in an Identity Provider (IdP).
If you are configuring IdP-based SSO for the first time, we recommend you use OIDC. Many identity providers offer better support for OIDC, because SAML is an older protocol.
Configuring SAML
For SAML to work your IdP and PostHog (SP) need to exchange information. To do this, you need to configure some settings in your IdP and on PostHog. Depending on your IdP you might need to pass PostHog information first, or the other way around. We provide complete examples for OneLogin and Okta below, but the general flow is:
If you are on self-hosted, make sure you have properly set up your
SITE_URLenvironment variable configuration.If you are on self-hosted, you will need to be running your PostHog instance over TLS.
Register a new SAML 2.0 application with your IdP. If you need to pass PostHog's information to your provider first, set the following values below (alternatively if your IdP supports it, you can obtain our XML metadata from
<yourdomain>/api/saml/metadata/orhttps://us.posthog.com/api/saml/metadata/for PostHog Cloud US orhttps://eu.posthog.com/api/saml/metadata/for PostHog Cloud EU)- Single Sign On URL (also called ACS Consumer URL):
<yourdomain>/complete/saml/orhttps://us.posthog.com/complete/saml/for PostHog Cloud US orhttps://eu.posthog.com/complete/saml/for PostHog Cloud EU. - Audience or Entity ID: Your Site URL value (verbatim), on PostHog Cloud this is
https://us.posthog.comorhttps://eu.posthog.com - RelayState: On PostHog cloud, get your RelayState value from the SAML configuration modal in your PostHog Organization settings. For self hosted, empty or default (will be set on every request).
- Single Sign On URL (also called ACS Consumer URL):
For SAML to work properly with PostHog, we need to receive at least the following information from your IdP in the SAML assertion payload: ID, email and first name. Optionally, you can also pass the last name. By default, PostHog expects these attributes with a certain name.
| Attribute | Default name on PostHog | Optional? |
|---|---|---|
| Permanent ID | name_id | ❌ No |
email | ❌ No | |
| First (Given) Name | first_name | ❌ No |
| Last Name (Surname) | last_name | ✅ Yes |
You will now need to obtain some parameters from your IdP and configure them in PostHog for the appropriate domain in Authentication domains. Depending on your provider, they may only provide this information as an XML metadata file. If this is the case, you can open the file in a text editor and obtain the required values from there.
- SAML Entity ID: Will be identified as EntityID or IdP issuer. This can vary greatly between providers, but it usually looks like a URL.
- If using Azure AD the setting to use for this field is called
Azure AD Identifier.
- If using Azure AD the setting to use for this field is called
- SAML ACS URL: The endpoint to which the SAML requests are posted. It's usually called SAML endpoint or IdP sign-on URL.
- SAML X.509 certificate: The public certificate used to validate SAML assertions from your IdP. It must be in X509 (almost all providers will provide it in this format). If your provider gives you the certificate as a file (usually
.pem), just open it with a text editor to get the contents. When setting this certificate be sure to keep any spaces and new lines (don't format it). The first and last line of the certificate (e.g.-----BEGIN CERTIFICATE-----) are optional.

- SAML Entity ID: Will be identified as EntityID or IdP issuer. This can vary greatly between providers, but it usually looks like a URL.
Once you've configured all the settings above, you can now log out and attempt logging in using SAML (you just need to enter your email address).
For security reasons, we don't output errors directly in your browser when something goes wrong. If you need help debugging on PostHog cloud, please contact support and provide the error ID that is shown at the bottom of the error page. To debug your self-hosted configuration, you have two options:
- Recommended. Check your app logs (this varies depending on your deployment). Any errors will be logged there.
- If everything else fails, temporarily set environment variable
DEBUG=1, errors will be fully displayed now in the browser. Please be sure to remove this once you're done, ugly things can happen if you don't.
Example: OneLogin
OneLogin quick setup
You can quickly connect OneLogin and PostHog by using the prebuilt integration.
In OneLogin admin, go to Applications and click Add App. Search for
PostHogand create your app.Go to the Configuration tab and where it says "PostHog domain name" enter your PostHog's instance domain (as it's also specified in the
SITE_URLenvironment variable), but don't include any protocol or trailing slashes. Examples:playground.posthog.com,myposthog.mydomain.com,myposthogdomain.com.Go to the SSO tab. This is where you'll obtain the information you need to pass to PostHog.
- Issuer URL needs to be set as SAML Entity ID.
- SAML 2.0 Endpoint (HTTP) needs to be set as SAML ACS URL.
- On X.509 Certificate click on View Details. Copy the full certificate and set it as SAML X.509 certificate.
You're good to go! Click Login with SSO in PostHog's login page.
OneLogin advanced
Use this option if you want to add additional configurations to your app that are not supported with the default app catalog.
In OneLogin admin, go to Applications and click Add App.
Search for
SAMLand select SAML Custom Connector (Advanced). Set name toPostHog.Go to the Configuration tab and edit the following attributes (leave everything else as default)
- In the Audience (EntityID) enter
https://us.posthog.com.- If you are using our EU deployment, use
https://eu.posthog.com. - If you are self-hosting, enter the exact same value as your
SITE_URLenvironment variable.
- If you are using our EU deployment, use
- Set the ACS (Consumer) URL Validator to a regex that only matches
<yourdomain>/complete/saml/. For instance:^https:\/\/us.posthog.com\/complete\/saml\/$(or useeufor an EU instance) - Set the ACS (Consumer) URL to
https://us.posthog.com/complete/saml/.- If you are using our EU deployment, use
https://eu.posthog.com/complete/saml/. - If you are self-hosting, use
<yourdomain>/complete/saml/.
- If you are using our EU deployment, use
- In the Audience (EntityID) enter
Go to the Parameters tab. You will add the following parameters. Be sure to check "Include in SAML assertion".
emailto match the user's email ("Email")first_nameto match the user's first name ("First Name")last_nameto match the user's last name ("Last Name")
Go to the SSO tab. This is where you'll obtain the information you need to pass to PostHog.
- Issuer URL needs to be set as SAML Entity ID.
- SAML 2.0 Endpoint (HTTP) needs to be set as SAML ACS URL.
- On X.509 Certificate click on View Details. Copy the full certificate, removing the first and last lines and set it as SAML X.509 certificate.
You're good to go! Click Login with SSO in the login page.
Example: Okta
In Okta admin, go to Applications and select Create App Integration.

Select the SAML 2.0 option for sign-in method.

Select Next, name the configuration PostHog, then select Next again.

Navigate to your PostHog organization's authentication settings, scroll down to SAML, then select Configure.


Copy the ACS consumer URL from PostHog into the Okta app's Single sign-on URL field, and copy the Audience / entity ID from PostHog into the Okta app's Audience URI (SP Entity ID) field.

In Okta, select Next. Check the box that says This is an internal app that we have created, then select Finish.

Copy the Sign on URL from Okta to the SAML ACS URL field in PostHog, the Issuer from Okta to the SAML entity ID field in PostHog, and the Signing Certificate from Okta to the SAML X.509 certificate field in PostHog.
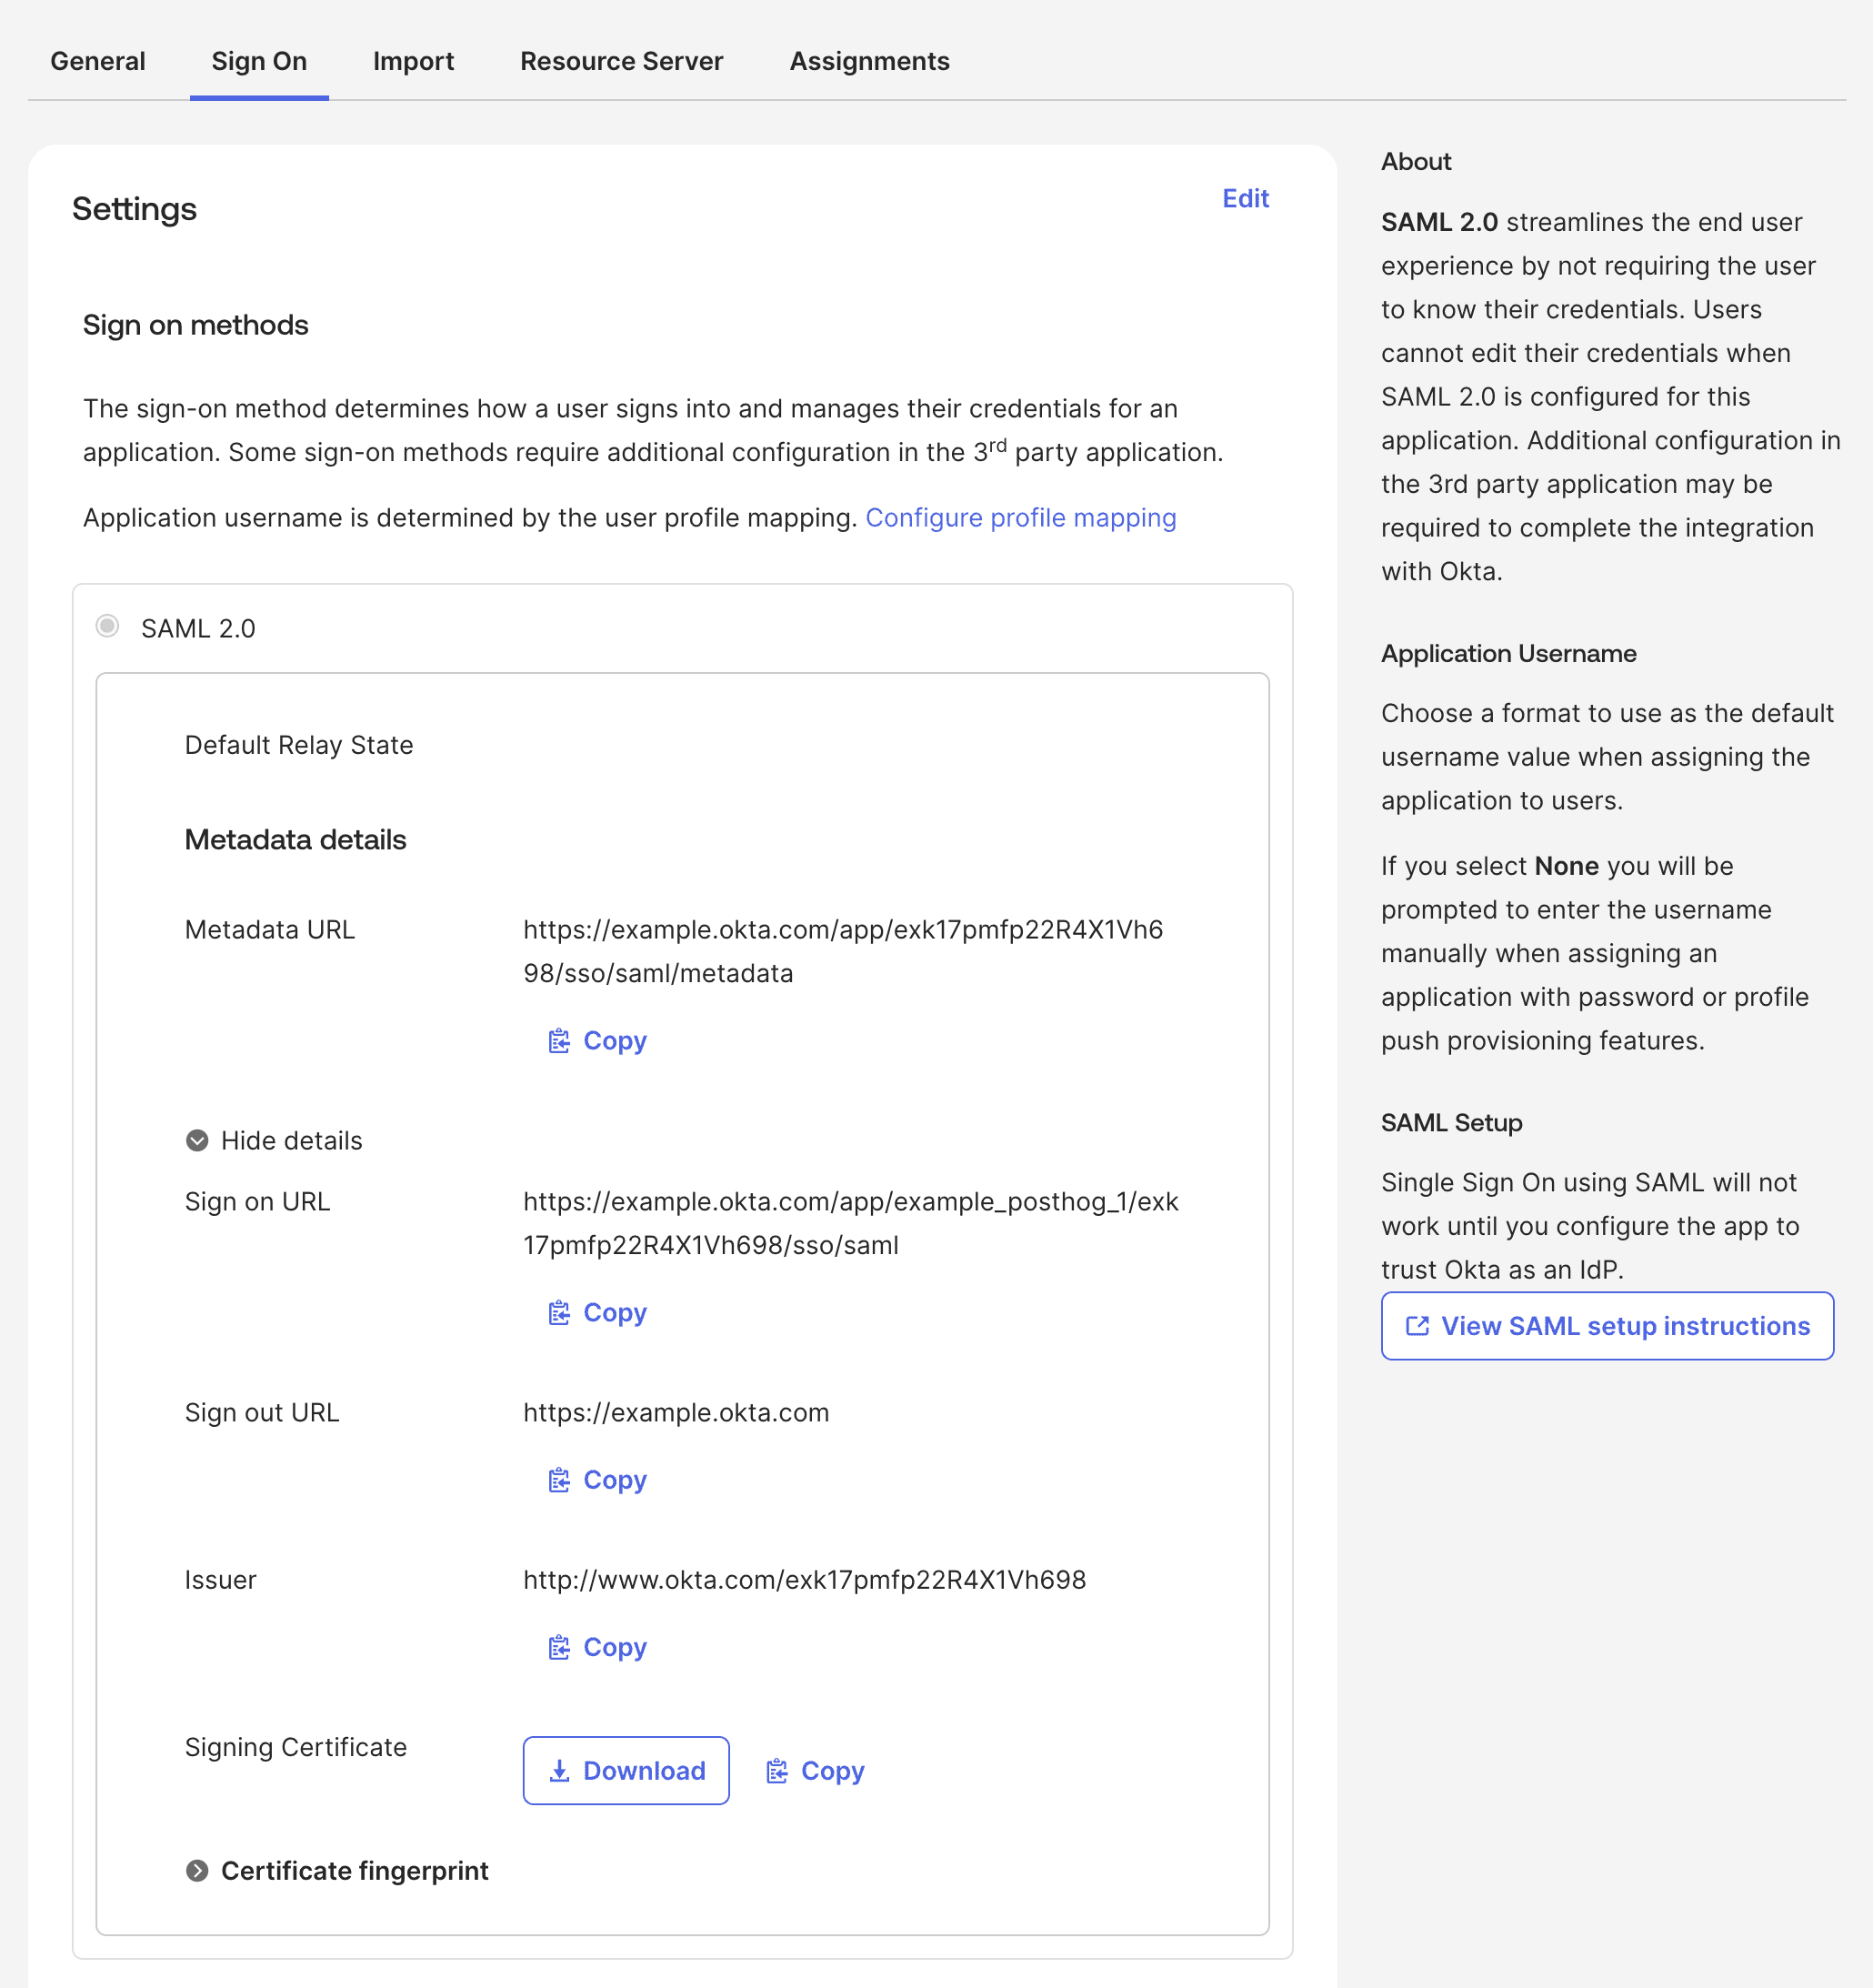
Select Save configuration in PostHog.


In Okta, navigate to the Sign On tab of your SAML app, then select Edit in the Settings section.
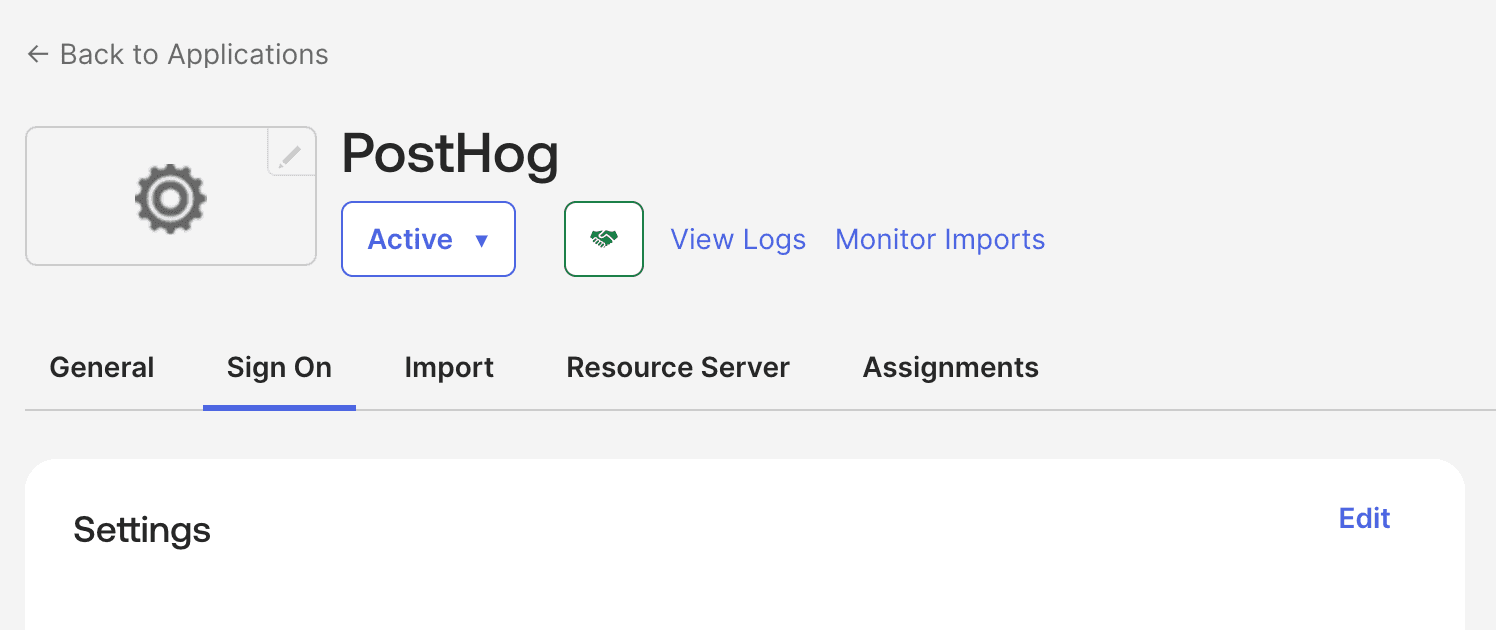
Copy the Relay state from PostHog to the Default Relay State field in Okta. Select Save

In Okta, scroll down to Attribute Statements add the following statements:
Name Expression email user.profile.email first_name user.profile.firstName last_name user.profile.lastName 
The next time you enter your email address during login, you will see an option to login using SAML.
Warnings
When using SAML to authenticate users in PostHog, there are a few considerations to keep in mind:
Only use SAML with identity providers you trust and that verify the user's email address. During login we use the email address provided by the identity provider. An untrusted identity provider could spoof a user's email address to impersonate your users.
Enabling or enforcing SAML will not disable Personal API Key usage. Users can authenticate with the PostHog API using their API keys without first authenticating via SAML. You can use ID-JAG (XAA) to programmatically restrict API access using policies defined in your identity provider.
Our SAML integration only handles authentication and user provisioning. It does not handle user removal. You can use SCIM to automatically deprovision users.
When you enable or enforce SAML, any existing user passwords are saved. If you disable SAML SSO in the future, your users will be able to login using their pre-existing password credentials.